


Every branch, every employee, one network
SecuryTik Overlay & VPN Automation
A self-hosted VPN hub for MikroTik branches and remote staff: routing, policies, DNS, monitoring and router management in one panel, on one VPS you own.
One routed network, no NAT inside
Your VPS becomes the hub. Every branch and every remote user reaches every other by its real address.
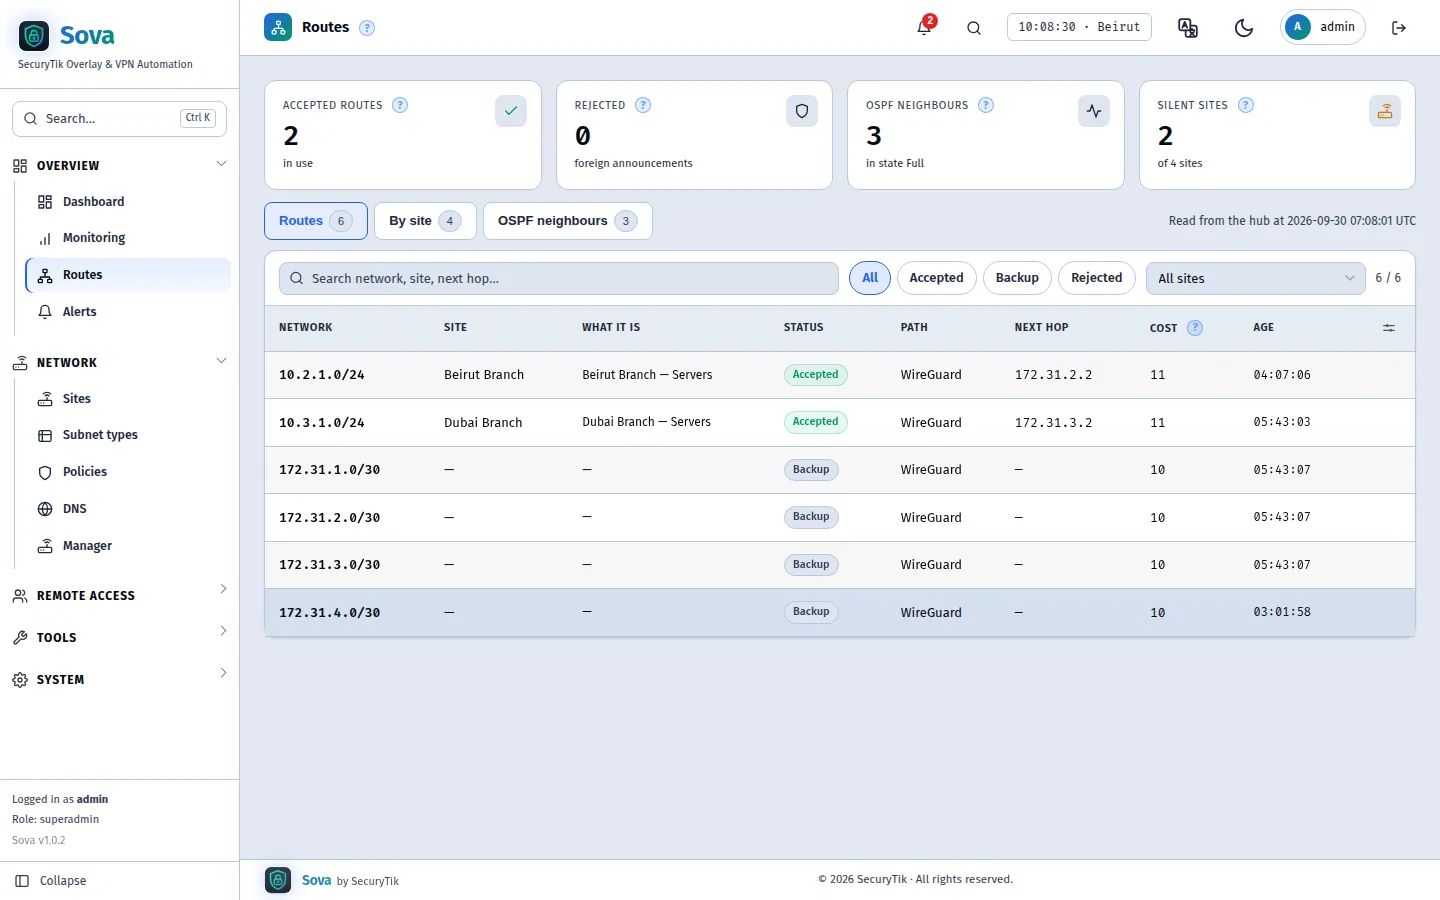
Hub-and-spoke WireGuard
- One tunnel per branch, dialled OUT from the branch — works behind NAT, CGNAT and 4G
- A port per site (51000 + site number); nothing to open at the branch
- No NAT between sites: logs, cameras and servers see real source addresses
L2TP/IPsec backup
- A second tunnel per branch, used automatically when WireGuard is blocked or down
- Failover in about 4 seconds, and back again by itself
- The dashboard shows which sites run on the backup path
OSPF routing
- Branches announce their networks; the hub learns and shares them
- A new branch is learned by every other branch without touching them
- Networks the branch admin adds by hand are shared too — per site, with a toggle
Route checks
- A branch may only announce addresses inside its own block
- Anything else is rejected at the hub and raises an alert — no route hijacking
- The Routes page shows accepted, backup and rejected networks with path and next hop
Sites talk directly, the hub is the safety net
Since SOVA 2.0, branches link router to router whenever their Internet connections allow it.
Full mesh, automatically
- A direct WireGuard link between every pair of sites that can reach each other
- The hub finds each site's public address and opens both NATs at once (UDP hole punching)
- Behind a symmetric NAT a site keeps using the hub — shown on its page
- "Reachable at": give a site a fixed public address or forwarded port by hand, for sites the hub cannot learn by itself
OSPF decides
- Direct first, then the hub, never through another branch
- A broken direct link is left in about 5 seconds and comes back by itself
- A flapping link is held on the hub; a lost one raises an alert
See it
- Direct links on the map and the GeoMap: solid when direct, dashed when on the hub
- Hub links / Direct links switches to show either
- Turn direct links off per site at any time
A branch in two minutes
Name it, tick the networks it needs, paste one line into the router.
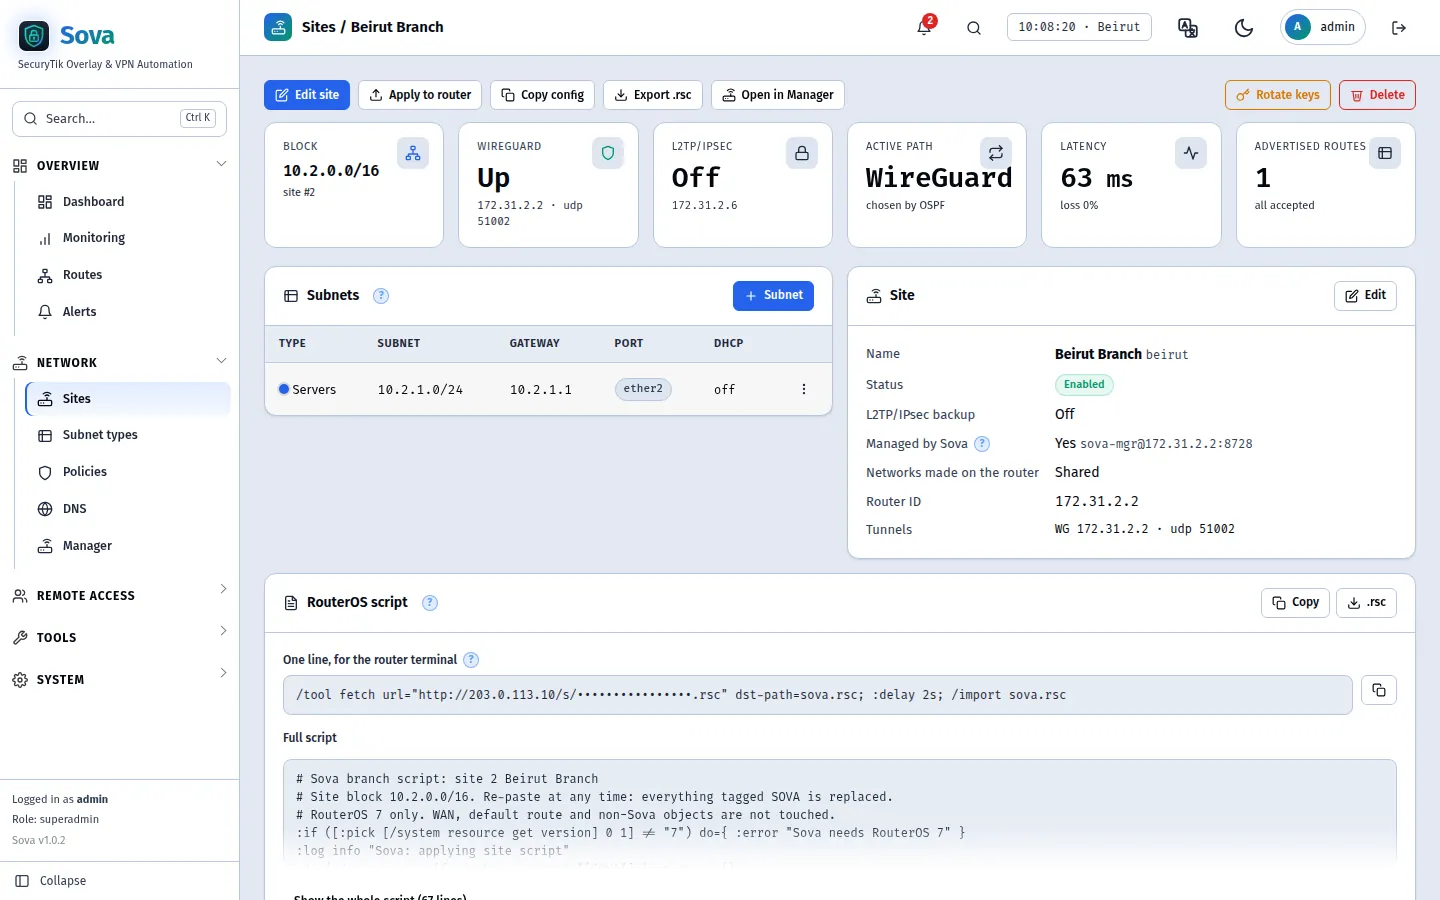
Derived addressing
- Site N owns 10.N.0.0/16; network types sit at the same third octet everywhere
- Servers are 10.1.1.x at site 1 and 10.2.1.x at site 2 — nothing to plan, nothing to collide
- One port per network, from ether2 upwards, with DHCP — no VLANs needed
Paste-ready RouterOS script
- One line to paste: the router fetches its script from the hub (single use, 24 hours)
- Checks the router first; never touches the WAN or the default route
- Safe to paste again at any time: everything tagged SOVA is replaced
Apply to router
- Managed branches get changes pushed over their tunnel — no re-pasting
- Add a network, move a port, rotate keys: one button
- Enable, disable, edit and delete from a SAMM-style list with bulk actions
Employees connect from anywhere
WireGuard app, the L2TP/IPsec client built into every phone and laptop, or OpenVPN for IP phones.
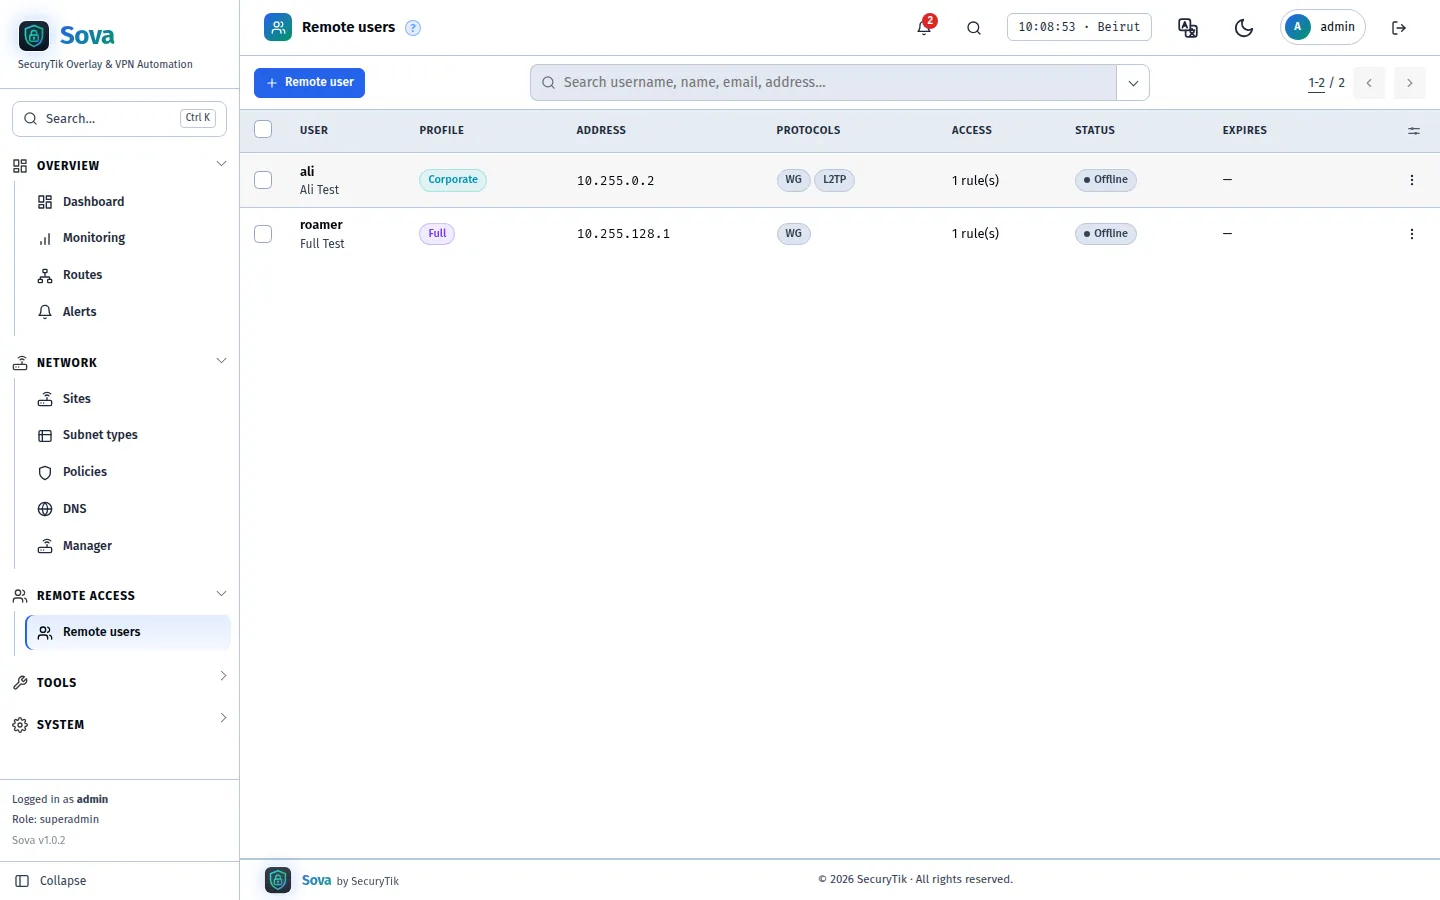
Two profiles
- Corporate: only company networks go through the VPN
- Full passthrough: all traffic leaves through the hub, with the hub's IP
- A fixed VPN address per user, so policies and logs know who it is
Per-user access
- The whole fleet, one site, one network type everywhere, or one network at one site
- Expiry dates; disabling disconnects at once
- New key and password in one click
Easy handover
- One-line installers for Windows and Ubuntu: Install, Connect, Disconnect and Remove, each a script to paste
- QR code for phones, .conf for computers
- Copy or export the WireGuard config and the L2TP details from the list or the user page
OpenVPN for IP phones
- Desk phones without WireGuard connect over OpenVPN, each with its own certificate
- ca.crt, client.crt and client.key to upload, or one .ovpn profile
- A new key locks the old certificate out at once
DNS per user
- The hub (internal names work), none, or your own servers
- Always-on phones keep their normal DNS for everyday browsing
Your phone system across every branch
Keep the PBX on a private network and reach it from every branch, desk phone and mobile — nothing opened on the Internet.
One PBX, every branch
- Branch phones register on the PBX by its private address
- PBXs in different cities trunk to each other inside the tunnels
- One public number, extension ranges and ring groups per branch
Extensions on mobiles
- A remote user per mobile with always-on WireGuard
- The vendor softphone points at the PBX directly — no vendor cloud plan for remote extensions
Small shops and kiosks
- A small MikroTik (hAP ax lite, or LTE6 with a 4G SIM) becomes a site
- An IP phone and the point-of-sale PC plug into it
Automate the PBX
- The API reaches the PBX's own web API through the hub
- No port forward, every call in the audit log
IP phones to your UCM, no cloud subscription
Phones at every branch, at home and on mobiles register on your own UCM over SOVA's tunnels — no vendor cloud plan, nothing opened on the Internet.
Every phone reaches the UCM
- Desk phones at branches register on the UCM by its private address
- Phones at home connect over OpenVPN, each with its own certificate
- The UCM itself is never exposed to the Internet
No cloud subscription
- No remote-connect or cloud plan from the phone vendor for remote extensions
- Calls travel between your sites and your own VPS only
- A new key locks a lost phone out at once
Mobiles too
- A remote user per mobile with always-on WireGuard
- The vendor softphone app points at the UCM directly
Who reaches what — including apps
Every site reaches every site by default. Rules are checked top to bottom, firewall style.
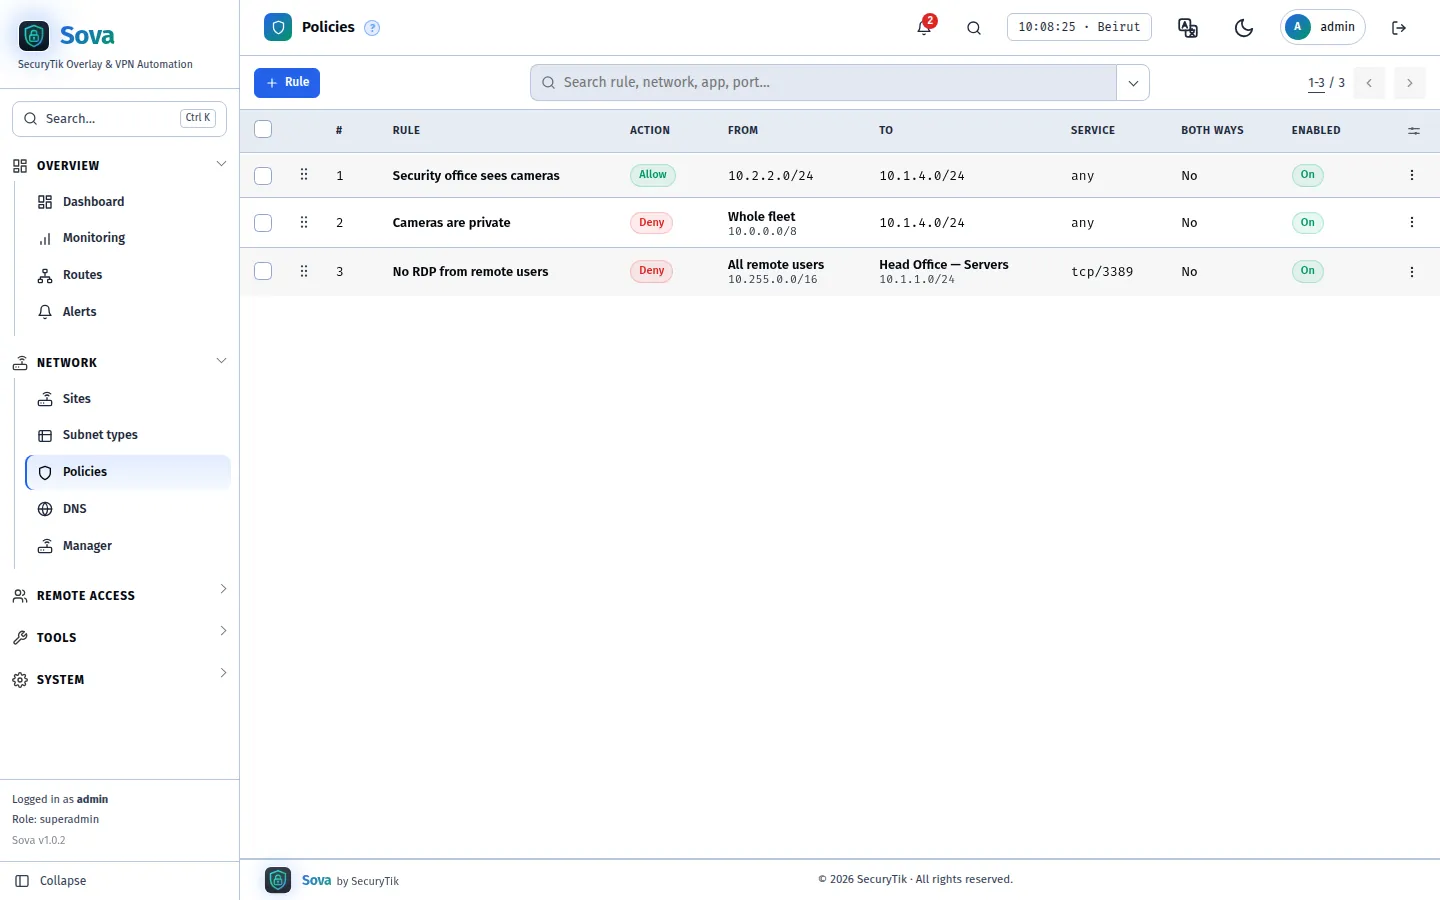
Enforced on the hub
- All branch-to-branch traffic crosses the hub, so a branch cannot bypass a rule
- Allow or deny by protocol and port, one way or both
- A new deny also cuts connections that are already open
Several sources and destinations
- Pick sites, networks, remote-user groups or addresses — as many as a rule needs
- Drag rules into order; the first match wins
- Search, filter, export, bulk enable/disable
App & website blocking
- Block TikTok, Instagram, games, streaming… for chosen networks
- Enforced on the branch router, where the branch's own internet is
- SOVA switches the app on in that router's filter for you
Every branch router, from one screen
The MikroTik Manager from SAMM, over the tunnels — no public IP, no port forwarding.
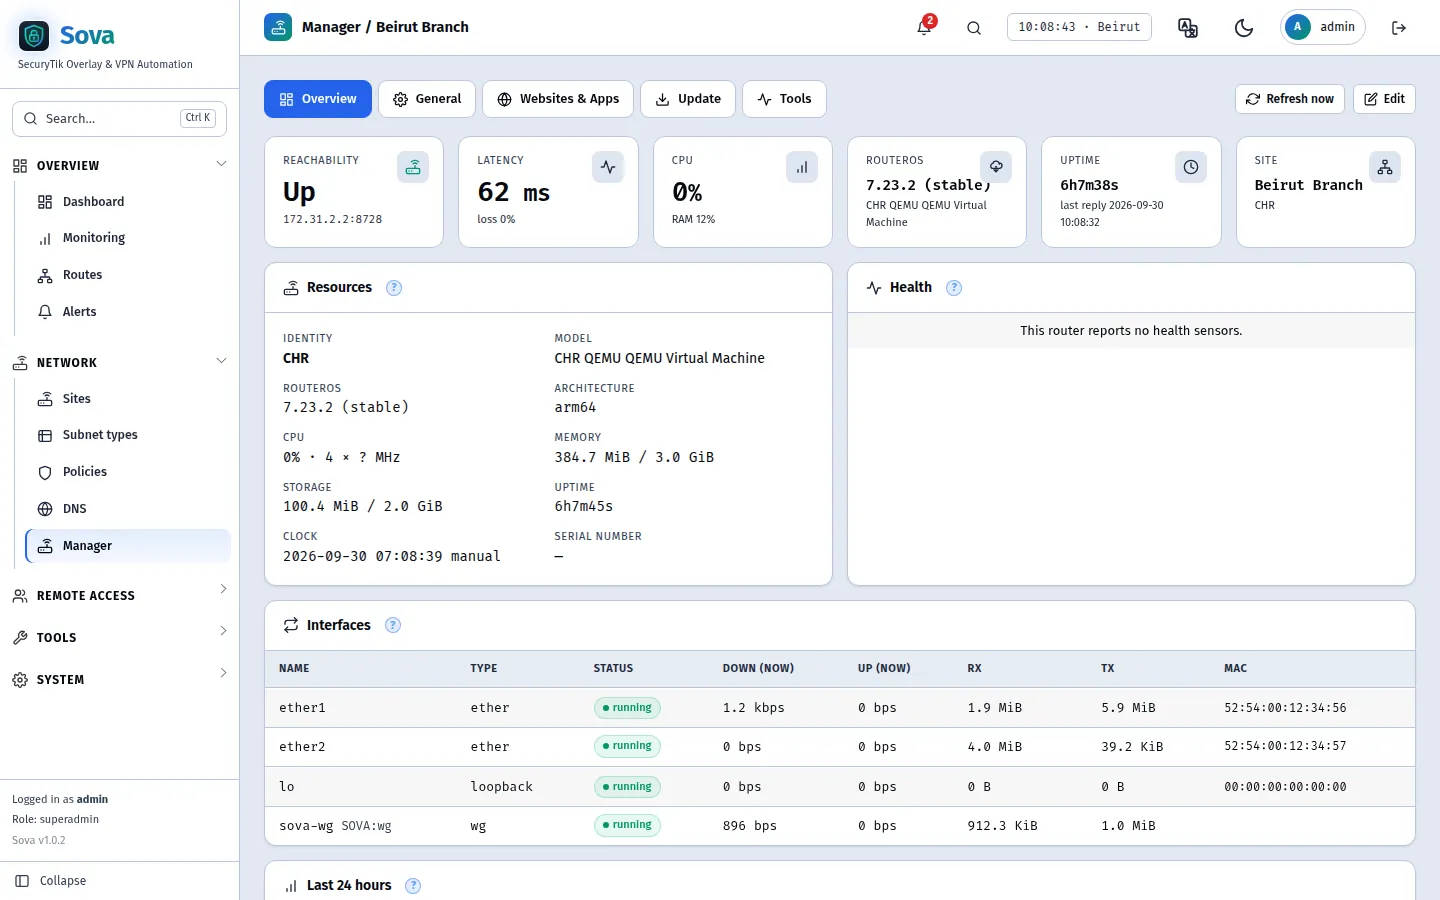
Health & control
- Model, RouterOS version, CPU, memory, uptime, interfaces live
- Time zone, NTP, DNS, reboot, RouterOS updates
- Ping and traceroute from the router or from the hub
Traffic history
- Interface traffic for every managed router, kept 30 days
- Traffic per app and website, with totals for any window
- Know what each branch uses without logging in to it
Bulk actions
- Tick routers and set time zone, NTP or DNS, update, back up or reboot
- A result per router
- Website & app filter per router, and blocks per network
Router security
- One click secures a branch router: Off, Normal or Advanced, the same lab-tested MikroTik rules as SAMM's Auto Security
- Normal: connection tracking, bogon drop, brute-force and service hardening. Advanced: adds DDoS, port-scan and rogue-DHCP protection, management locked to the fleet
- Every switch can be set on its own; every change is backed up and checked before it is kept
Know before the branch calls
Latency, loss and traffic for every tunnel, checked every 30 seconds.
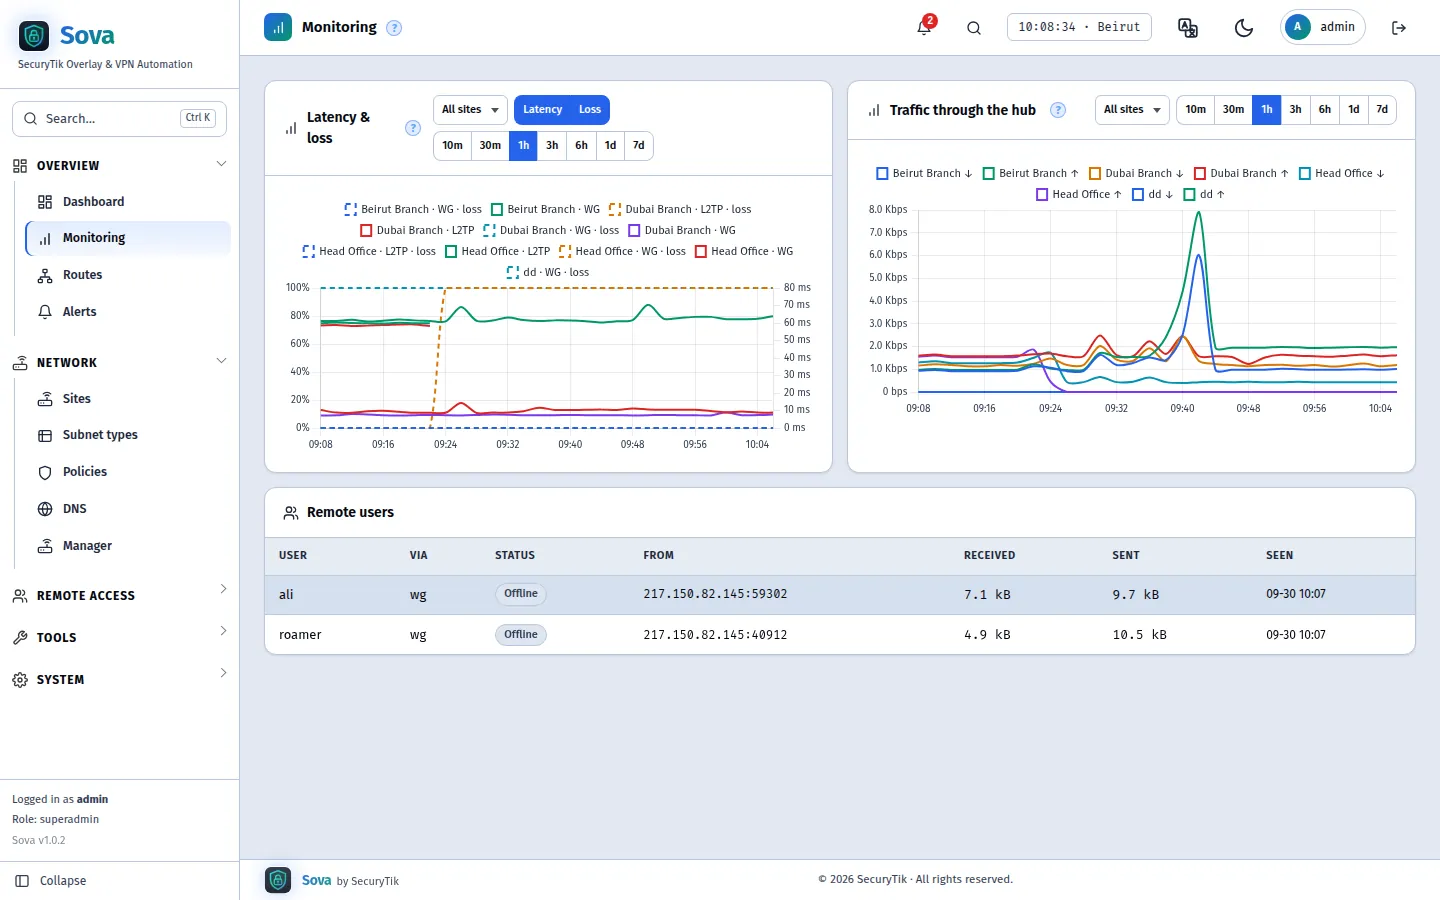
Charts & dashboards
- Dashboard blocks you drag, resize and save as several dashboards
- Windows from 10 minutes to 7 days, per site or for all
- Remote users online, with their traffic
Live traffic
- One chart for the whole fleet that keeps moving: site to hub, site to site over direct links, site to Internet, hub to Internet, remote access
- Read every 1 to 30 seconds, filter by site, direction and type, keep only the busiest lines
- Bookmarks remember your picks, including which lines are selected
Alerts
- Site down, on backup path, foreign routes, router unreachable, hub apply failed
- Licence reminders 30, 14, 7, 3 and 1 days before the plan ends
- “I am on it” and quiet for an hour or a day — the SAMM alert log
- Every alert resolves by itself when the problem clears
Notification center
- Telegram, email and WhatsApp Cloud API
- Choose which events go to which channel
- An outbox with every message sent or failed
- Announcements from SecuryTik — news and product messages — pop up on the dashboard by themselves
Names instead of numbers
The hub answers for your internal zone; everything else goes to public DNS.
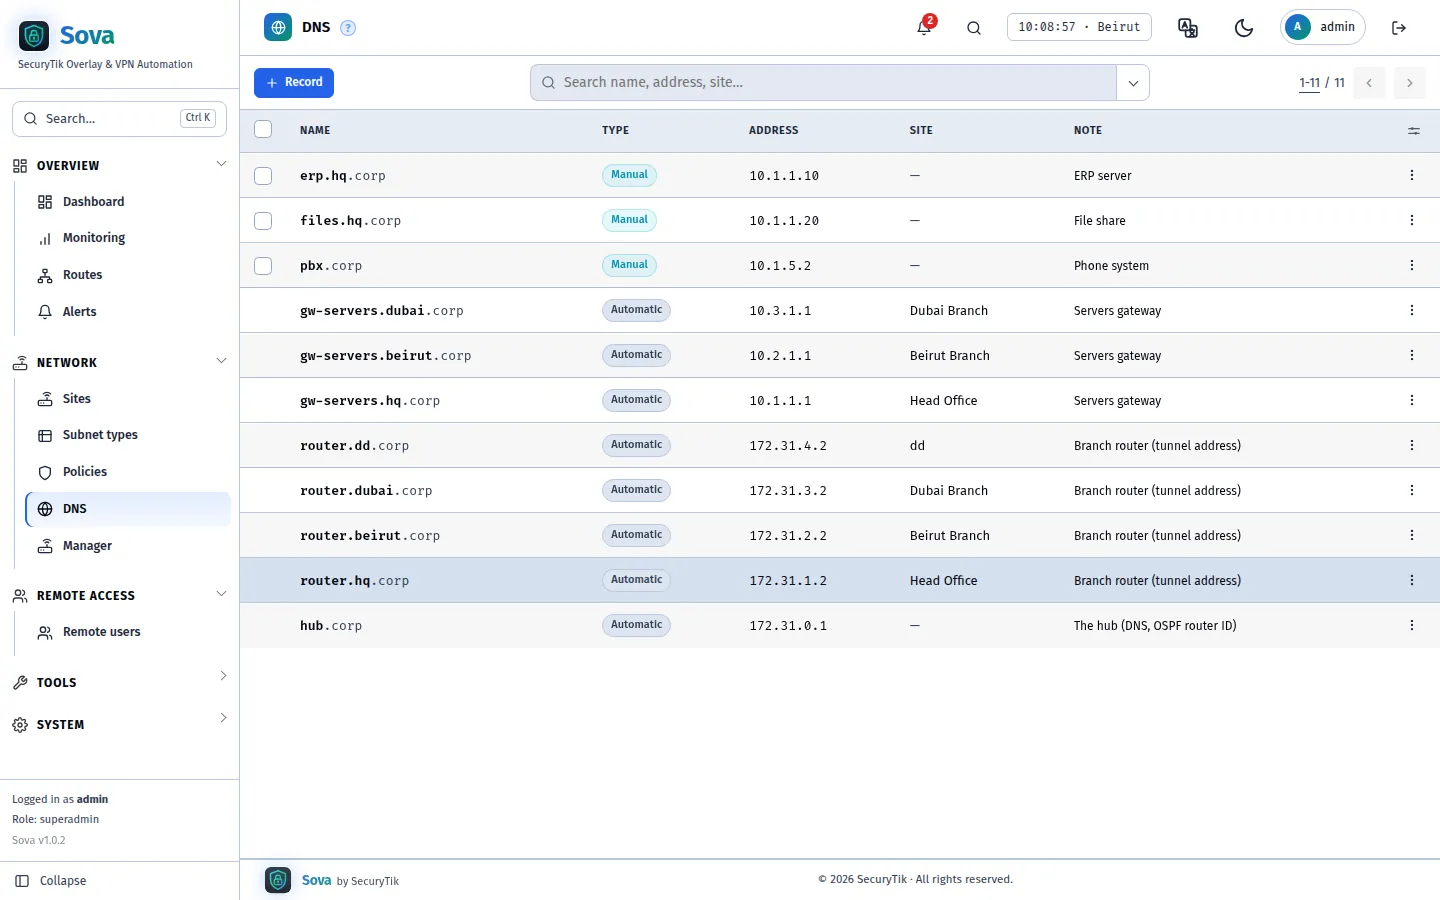
Automatic names
- router.
. and gw- . . for every branch - Branch DHCP and remote users get the hub as DNS
- Works over either tunnel
Your own records
- erp.hq.corp → 10.1.1.10 in one pop-up
- Automatic and manual names in one searchable list
- Export to CSV or Excel
Every device, its name, its port
Leases and ARP tables of every branch router, in one searchable list.
Devices & static leases
- Every device behind every managed branch, online or not
- Make a lease static or move it to a new address in one click
- A DNS name that follows the device when its address changes
Port forwards
- A port on the hub's public address to a device or a DNS name in any site
- The device sees the caller's real address
- Hit count and a log of every connection, with export
Wake on LAN
- Wake a computer from the panel, through its own branch router
- Or let the router wake it when a connection heads its way
- Bulk wake for a whole list
Performance
- Speed and ping between every pair: sites, the hub and the Internet
- Ping, traceroute and speed tests drawn live on the map
- Hints when a router's CPU, one site's upload or a lossy line is the limit
Built to be run by a team
The same administration tools SAMM customers already know.
Admins, roles & audit
- Per-area view / edit permissions; Super Admin, Manager, Monitor
- Every change in the audit log — who, when, from where
- Password recovery by email, and a reset tool for lockouts
API & webhooks
- REST API with scoped tokens: sites, remote users, policies, DNS, stats, devices
- Reach devices inside the branches over HTTP(S) through the hub — for automation that can only use ports 80 and 443
- QR codes and OpenVPN files for remote users, licence end date and days left
- Support API: diagnose and fix a hub and its routers without a shell on it, same scopes as SAMM's router API
- Signed webhooks for site, user and alert events
- Interactive reference at /api/v1/docs
Move to a new server
- A whole hub — sites, keys, users, licence — to a new VPS from two browser windows
- Routers keep working and switch one by one; a router that cannot reach the new server comes back by itself
- The old server resets itself to a fresh install, backups erased; the licence moves with the hub
High availability
- Two or more servers as one cluster: one active, the others keep a live copy
- The active server stops: a standby takes over in about 30 seconds and routers follow by themselves
- Add, hand over to or remove a node from any node's panel; one licence covers the whole cluster
Backup, updates, Cloudflare
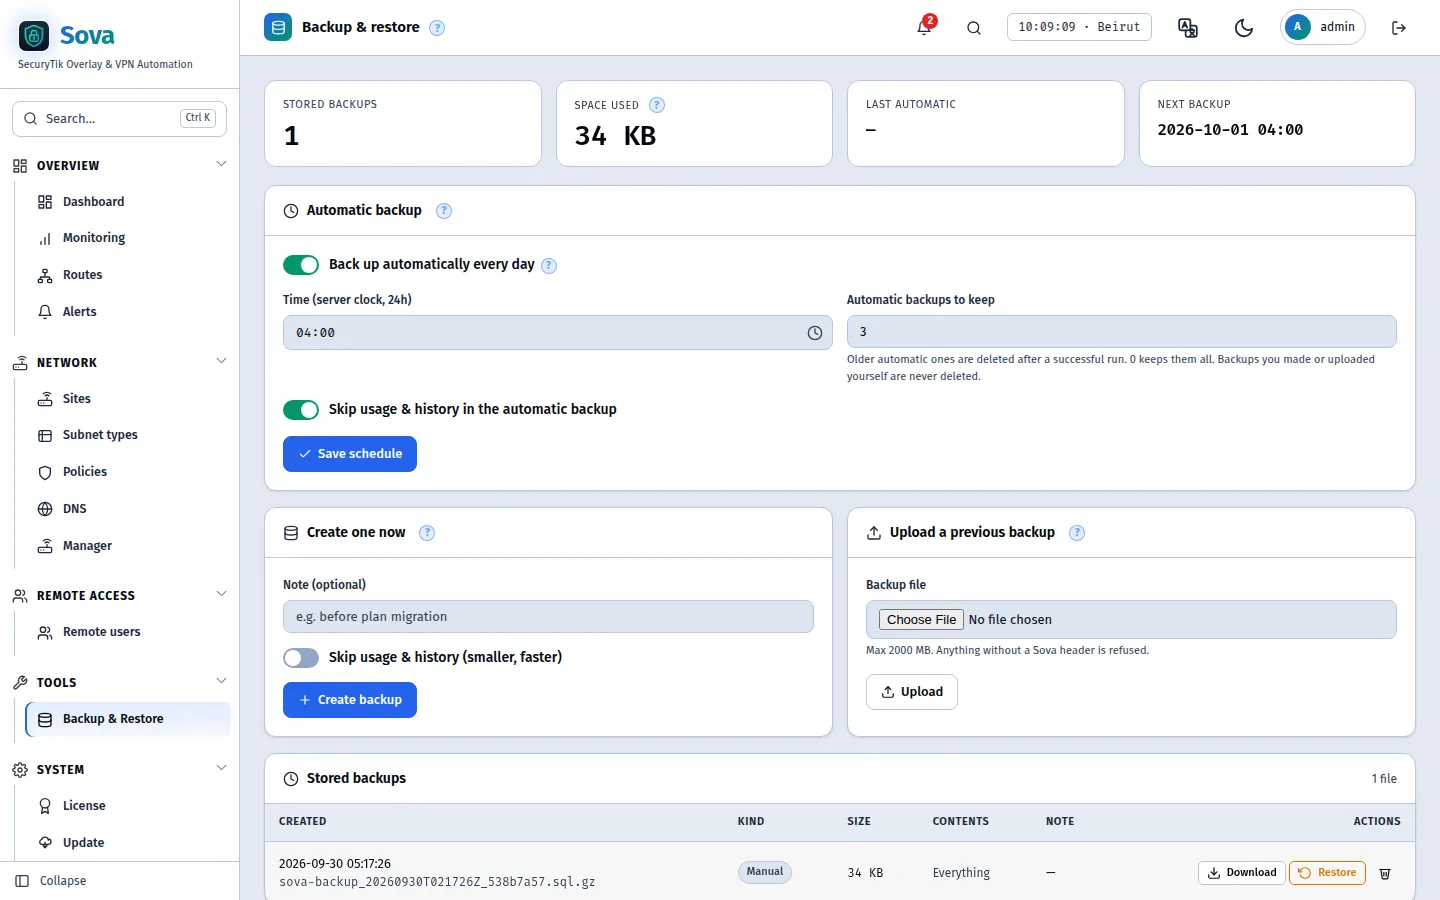
- Scheduled backups with retention; restore in one click
- Signed updates from the panel — tunnels keep running
- HTTPS on your own domain through Cloudflare Tunnel